Claude Code Leaked 512K Lines of Source Code Because of One Forgotten File
 Claude Code Leaked 512K Lines of Source Code Because of One Forgotten File
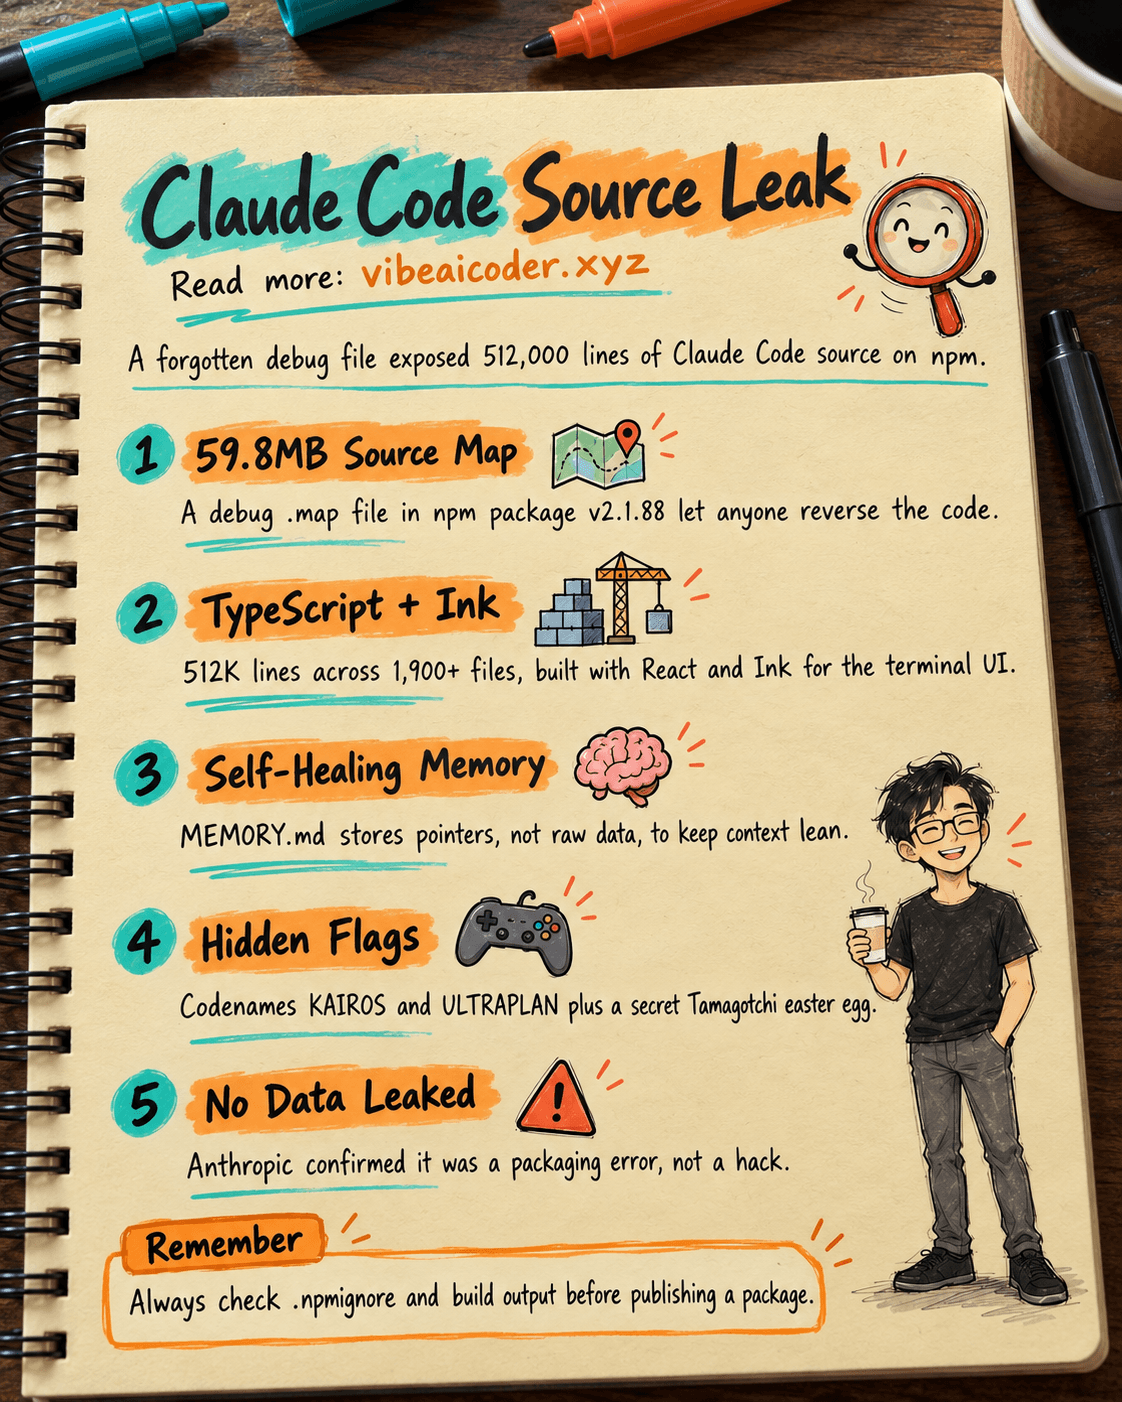
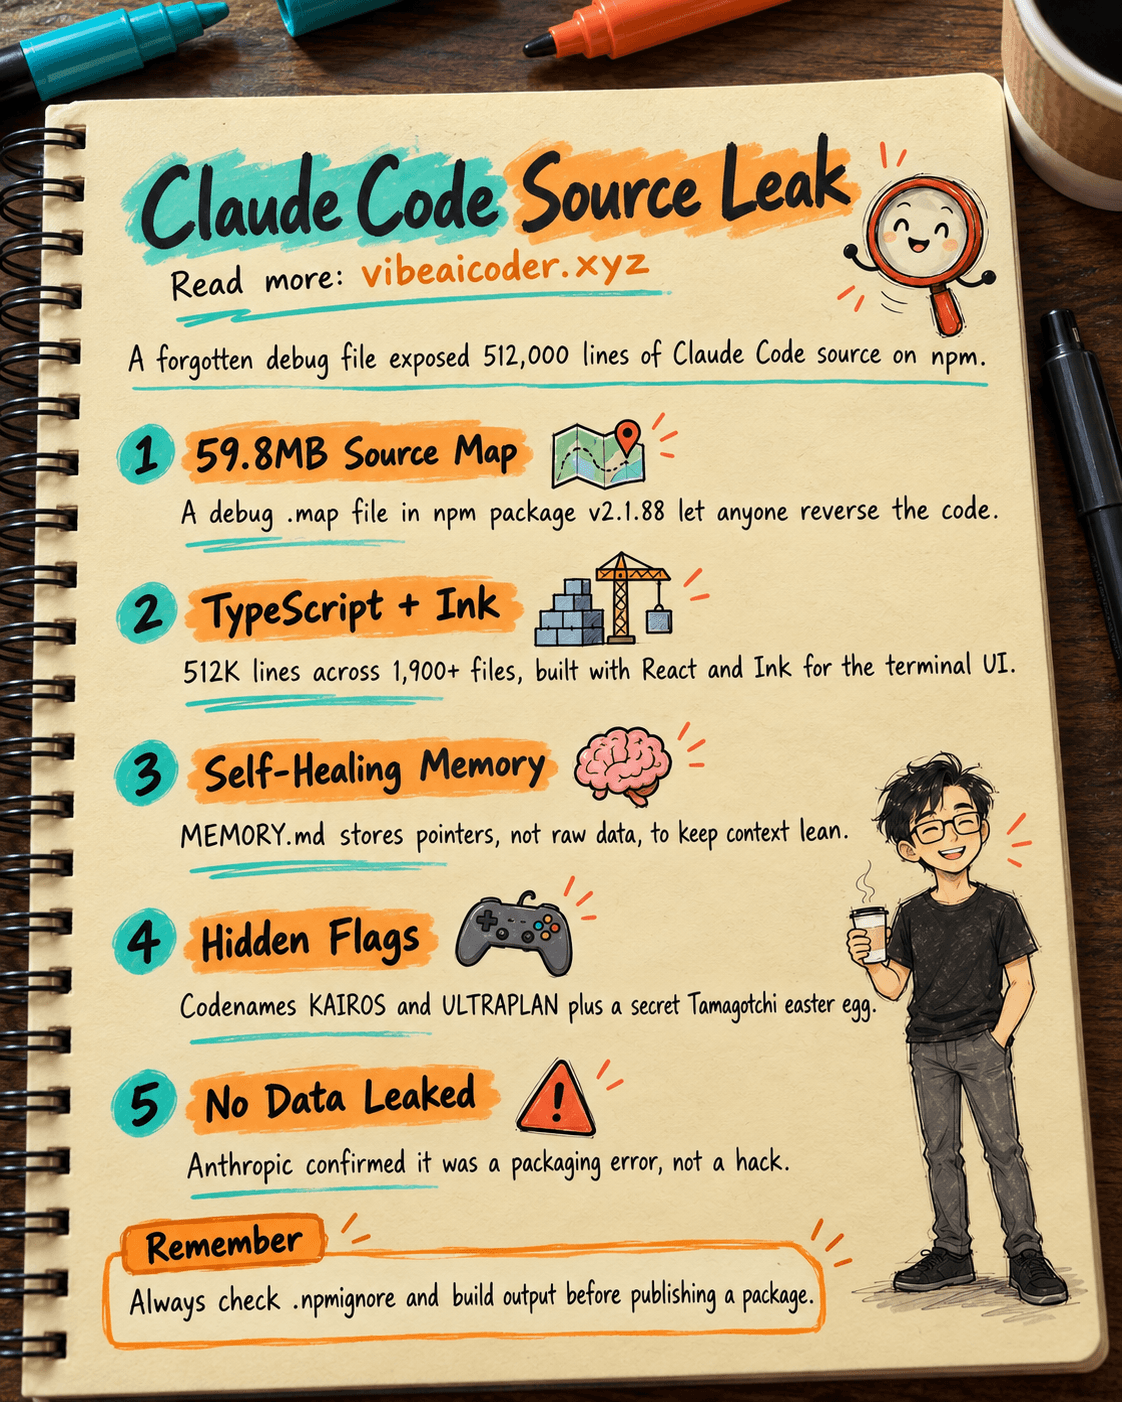
Anthropic just made a mistake every developer dreads: forgetting to strip a debug file before publishing to npm. The result? The entire Claude Code source tree sat out in the open for anyone to read.
 What happened
On March 31, 2026, the community discovered that the npm package @anthropic-ai/claude-code, version 2.1.88, shipped with a source map file (.map) weighing in at 59.8MB. Source maps exist purely for debugging, but this one let anyone reverse the entire original source code. The end result was that roughly 512,000 lines of TypeScript spread across more than 1,900 files were fully exposed.
 What is actually inside Claude Code
For the first time, developers got a look at the guts of a leading AI coding agent. Claude Code runs on TypeScript and uses React + Ink to render its interface right inside the terminal. The largest file, QueryEngine.ts, weighs in at roughly 46,000 lines and manages the entire engine for calling the LLM, streaming responses, and counting tokens.
The memory system uses a Self-Healing Memory architecture, storing state in a MEMORY.md file as pointers rather than stuffing raw data straight into the context window. There is also a multi-agent orchestrator built on a coordinator-worker pattern, plus a three-tier context compression system made up of MicroCompact, AutoCompact, and Full Compact.
 Interesting finds
The source code also revealed hidden feature flags that had never been announced. Two mysterious codenames, "KAIROS" and "ULTRAPLAN", turned up in the code, leading the community to speculate they point to some kind of automated agent planning feature. Even more amusing, a hidden Tamagotchi style virtual pet feature was buried in there too, likely an easter egg the Anthropic team built just for fun.
 Security risk
Anthropic confirmed this was purely a human packaging error, not a security attack. No customer data or credentials were exposed. Still, security researchers warned that exposing the logic behind Hooks and MCP (Model Context Protocol) could help bad actors craft malicious repositories designed to trick an agent into running unauthorized commands or exfiltrating data. On top of that, around the same time there were reports of a supply chain attack targeting the axios package, which happens to be a dependency of Claude Code.
 The lesson for developers
This incident is a reminder to every developer: always double check your .npmignore file and build configuration before publishing. The Bun runtime generates source maps by default, and if you don't exclude them properly, your source code ships right along with the package. One small gap in a CI/CD pipeline can turn into a major incident within a matter of hours.
More articles

Gemini 4 Argon Reads a 500-Page Chemistry Patent in One Afternoon

Claude Opus 5.5 Codes a Real Money Trading Game in One Day

What Is a Token in AI? Why ChatGPT and Claude Charge by Tokens

What Is Chain of Thought? Why Asking AI to Think Step by Step Works Better

Claude Sonnet 5.5 vs GPT-6.1 Sol: Which AI Model Is Worth Using?
 Claude Opus 5.5 Launches: 30% Faster, 40% Cheaper, Blocks AI Brain Copying